Crypto Users Lose $9.5M to Fake Ledger App on Apple Store
TL;DR
- A fake Ledger app on Apple’s App Store was used to steal about $9.5 million from more than 50 crypto users in one week.
- Victims lost funds after entering seed phrases into the malicious app, enabling attackers to drain wallets across multiple blockchains.
- Traced funds moved through exchange-linked addresses, highlighting ongoing risks in app distribution and crypto security practices.
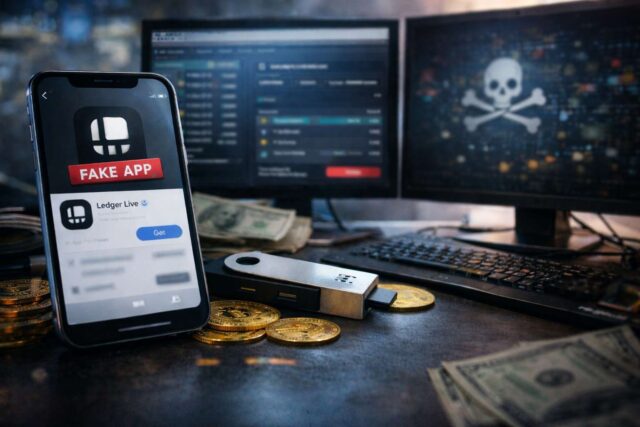
A fake Ledger app listed on the Apple App Store has been linked to a coordinated crypto theft that drained approximately $9.5 million from more than 50 users in under a week. The incident highlights how a single malicious listing can bypass user caution when distributed through a trusted platform.
The attack appears to have taken place between April 7 and April 13, with victims unknowingly entering their wallet recovery phrases into the fraudulent interface. Once exposed, attackers gained full control of funds stored across multiple blockchain networks.
How the phishing operation worked
The scheme relied on impersonating Ledger Live, the official software used to manage hardware wallets from Ledger. Users downloading the fake Ledger app were prompted to input their seed phrase. These critical security credentials, however, should never be shared or entered outside secure device workflows.
Once entered, attackers could immediately access and transfer funds. Reports indicate losses spanning Bitcoin, Ethereum-compatible assets, Tron, Solana, and XRP. The pattern suggests a broad and automated draining operation rather than isolated incidents.
One widely cited case involved musician Garrett Dutton, who reported losing 5.9 BTC after installing the malicious app. His experience became a public example of how even long-term holders can be compromised when trust is misplaced at the distribution level.
KuCoin flows raise laundering questions
Blockchain analysis shared by ZachXBT indicates that the attackers routed stolen funds through more than 150 deposit addresses associated with KuCoin. Reports describe these flows as part of a laundering process tied to the theft, bringing attention to how illicit funds can move through centralized exchange infrastructure.
There is no public evidence that KuCoin knowingly facilitated the activity. The findings are based on address tracing, which does not on its own establish intent or direct involvement. However, the scale of the flows has renewed focus on transaction monitoring and compliance controls across exchanges.
Platform trust under scrutiny
The incident places renewed pressure on Apple’s App Store review process. The presence of a fake Ledger app on a tightly controlled marketplace challenges the assumption that official app stores provide a baseline level of security.
For many users, especially those new to crypto, app store availability often equals implicit verification. This case demonstrates that attackers continue to exploit that trust layer. Phishing tactics are shifting away from obvious scam websites toward more credible distribution channels.
Ledger has reiterated that users should only download Ledger Live from its official website. Further, never enter recovery phrases into any app interface. The company maintains that its hardware devices remain secure when used correctly. Sadly, the seed phrase exposure remains the primary attack vector in such incidents.
Security risks extend beyond crypto-native platforms
The fake Ledger app case underscores a broader issue in crypto security: user protection often depends on behaviors outside the blockchain itself. While wallet technology may be robust, weak points emerge when users interact with third-party platforms or compromised software environments.
The scale and speed of the theft suggest a well-organized campaign that capitalized on both technical execution and user trust. It also reinforces a recurring pattern where attackers target onboarding friction points rather than attempting to break underlying cryptographic systems.
>>> Related: Ledger and Trezor Seed Phrase Mail Scam
What comes next
The full scope of the operation is still being assessed, and it remains unclear whether additional victims will come forward. Questions also remain about how long the malicious app was live and whether safeguards failed during the review process.
As the fake Ledger app incident continues to unfold, it is likely to intensify scrutiny on both app store governance and exchange-level monitoring. For users, the takeaway is more immediate. It illustrates that even trusted platforms do not eliminate the need for strict self-custody practices and verification of software sources.
The episode may not change how blockchains operate, but it directly affects how users interact with them. That makes it a practical security story, not just a technical one.