Home Blog Page 15

Dango Ends Trading as August 13 Shutdown Deadline Approaches
TL;DR

  • The Dango shutdown reached its first major deadline when perpetuals trading stopped July 29.
  • Remaining positions were due to close at oracle prices, while balances and vault deposits were supposed to move into spot accounts as USDC.
  • The Layer 1 network remains scheduled to close August 13, but Dango has not published a final settlement reconciliation.

Decentralized exchange Dango stopped perpetuals trading on July 29 at 12:00 UTC, completing the first major step in its planned two-stage shutdown. The platform said it would close remaining positions at oracle prices under its shutdown plan, while deposits in its liquidity vault would unlock for withdrawal.

Users now have about two weeks before the project plans to switch off its Layer 1 blockchain. Dango says it will return balances in USDC. Assets still on the network after August 13 are expected to return to their original Ethereum deposit addresses.

The trading cutoff triggered automatic settlement

Dango announced the closure on July 24 after concluding that it had no viable path to lasting commercial success. It gave traders five days to close positions and withdraw funds before trading ended.

The team warned that liquidity could become thin during that period. With fewer orders available to absorb trades, execution prices can worsen, especially for larger positions. As a result, Dango encouraged users to act before the cutoff instead of relying on the final settlement.

When trading halted on July 29, Dango said it would settle remaining positions using oracle prices, external price data an exchange relies on when its own order book cannot supply a fair reference. The company has not published those prices, so the settlement has not been independently verified.

Dango also said deposits in its DLP liquidity vault, a pooled system used to support trading activity, would unlock. It planned to move those funds and other balances into users’ spot accounts as USDC, a dollar-linked stablecoin.

The blockchain remains scheduled to close August 13

While trading has ended, Dango’s Layer 1 blockchain will remain available until August 13 at 12:00 UTC. Users can still withdraw during this final period, and deposits remaining at the chain cutoff are expected to return automatically to the Ethereum addresses from which they originally arrived.

That approach may reduce the risk of funds becoming permanently stranded. However, the announcement does not explain how the project will handle unusual deposit routes or unsupported assets, and it does not disclose current withdrawal times or the total value still awaiting removal.

Until Dango discloses how it will handle those edge cases, users with anything other than a standard deposit have no confirmed path to recovering their funds.

Dango is closing only months after launch

Dango was built as a decentralized venue for perpetual futures, which allow traders to speculate on asset prices without a fixed expiry date. It operated its own blockchain and promoted features such as unified margin, which lets traders use a single balance across positions, and an onchain order book.

The exchange launched its perpetuals product in April 2026. Before the shutdown announcement, independent reporting placed its total value locked near $1.6 million. The project had raised $3.6 million in a 2024 seed round led by Hack VC and Lemniscap.

Founder Larry Engineer attributed the closure to several pressures. He cited a shrinking financial runway, legal and compliance delays, lost momentum, staff departures, and difficult market conditions. Dango has not announced a bankruptcy filing or said that it cannot meet customer obligations.

The platform also suffered a security incident days after its April launch, when an exploit briefly drained funds from its insurance fund. The attacker returned the money in full for a bug bounty, and no users were affected. Dango did not cite the episode among its reasons for shutting down.

Users still need proof that settlement finished

While Dango’s plan described an orderly wind-down after trading ended, the shutdown process remains incomplete and operational results unconfirmed. The project has not published the oracle prices used for each forced closure or provided a reconciliation showing that all vault deposits reached spot accounts. It has also not disclosed how many customers still hold balances on the network. Nor has it said when, or if, those records will be released.
Triple-A Reports Treasury Loss as Investigators Track Extended Sweep

TL;DR

  • Triple-A lost an estimated $11.8 million in a hot wallet incident tracked across multiple blockchains.
  • Investigators observed deposits continuing to reach affected wallets and being swept for at least 31 hours after the first transfers.
  • Triple-A said the loss involved treasury assets, not client funds, but key details including access method and final loss remain undisclosed.

Crypto payments company Triple-A lost an estimated $11.8 million from its hot wallets in an incident first flagged by blockchain investigator Specter on July 24. Deposits kept arriving at the affected wallets and being swept for at least 31 hours after the first unauthorized transfers. Triple-A has since said the loss hit company treasury assets, not client funds. However, the access method and a final confirmed loss figure remain undisclosed.

What investigators tracked, July 24–26

Specter first reported the activity at 5:18 p.m. ET on July 24, saying more than $9.3 million had been taken, converted and bridged to Ethereum. PeckShield followed roughly four and a half hours later, raising the estimate above $9.7 million. It identified activity across Ethereum, TRON, Polygon, Arbitrum, Solana and The Open Network. PeckShield’s alert included a snapshot of eight transfers reaching a single Ethereum address between 20:35 UTC on July 24 and 03:03 UTC on July 25. It held 5,226.67 ETH, then valued at about $9.73 million.

By July 26, Specter had added Bitcoin to the list of affected networks, attributing another $1.8 million in losses to Bitcoin and TRON. That brought the estimated total to approximately $11.8 million. The investigator also reported that new deposits were still reaching the affected wallets and being swept 31 hours after the first large outflows appeared.

Triple-A’s only public comment during this window came on July 25, when the company told reporters it was actively investigating the wallet incident. At the time it assured that the attack had not affected customer funds. It did not elaborate on what the wallets held, how access had occurred, or whether the activity had stopped. The loss figures are based on on-chain tracking and not a confirmed company accounting. Triple-A has not confirmed the loss estimate or published a list of affected addresses.

Triple-A’s account, July 27

Roughly 35 hours after Specter’s initial alert, Triple-A published a newsroom statement addressing the wallet incident directly. The company said the affected wallets held its own treasury assets and no client funds. Client funds, it said, are held separately in trust accounts that were not exposed, consistent with Singapore’s rules requiring licensed digital payment token providers to safeguard customer assets apart from company holdings. Triple A Technologies Pte. Ltd., the company’s Singapore entity, holds a major payment institution licence from the Monetary Authority of Singapore.

The statement also said the company detected unauthorized access on July 25. Subsequently, it placed some services into maintenance mode for about three hours while securing the affected infrastructure. Once it completed additional security checks, normal processing resumed. Triple-A said it is working with cybersecurity firms and the Singapore Police Force, and that it remains well-capitalized and able to meet its liabilities. The financial impact would be absorbed through treasury reserves.

The statement did not disclose a specific loss figure, wallet addresses, or how the unauthorized access occurred.

Where the two accounts do not line up

Triple-A’s description of a three-hour maintenance window on July 25 sits awkwardly next to Specter’s report of deposits still being swept 31 hours later, into July 26. Businesses often continue sending funds to previously issued deposit addresses until those addresses are replaced. If a compromised address remains active, additional deposits can keep reaching an attacker well after the initial breach has been identified and contained elsewhere.

Pausing certain services is not the same as disabling on-chain deposit addresses. Also, Triple-A has not specified which systems underwent the maintenance period or whether it rotated any deposit addresses. The two timelines are not necessarily contradictory, since a brief pause to secure core infrastructure would not automatically stop funds from landing on addresses still in circulation. But nothing in Triple-A’s statement accounts for the extended sweep Specter described, and the company has not addressed the gap directly.

Still open

Several questions remain unanswered. Triple-A has not disclosed whether stolen credentials, compromised private keys or another failure allowed the transfers, nor has it published a final loss figure or the specific wallet addresses involved. It has also not said whether any exchanges or stablecoin issuers froze funds linked to the incident, or whether it recovered any assets.

As of publication, two days after Triple-A’s July 27 statement, no further update has confirmed whether the sweeping of new deposits described by Specter has stopped.

Why Bitcoin Developers Are Divided Over BIP-110’s New Restrictions

TL;DR

  • The Bitcoin BIP-110 proposal would temporarily restrict several methods of attaching non-payment data to transactions.
  • Supporters say the rules would reduce costs for node operators, while critics warn they could disrupt valid transactions and set a filtering precedent.
  • Miner support remained below 1% as of July 18–19, ahead of an enforcement stage expected to begin in August.

A dispute over BIP-110, a proposed temporary change to Bitcoin’s transaction rules, is moving toward a scheduled enforcement test in August. The debate now includes prominent developers, infrastructure operators, security specialists and corporate Bitcoin advocates on both sides.

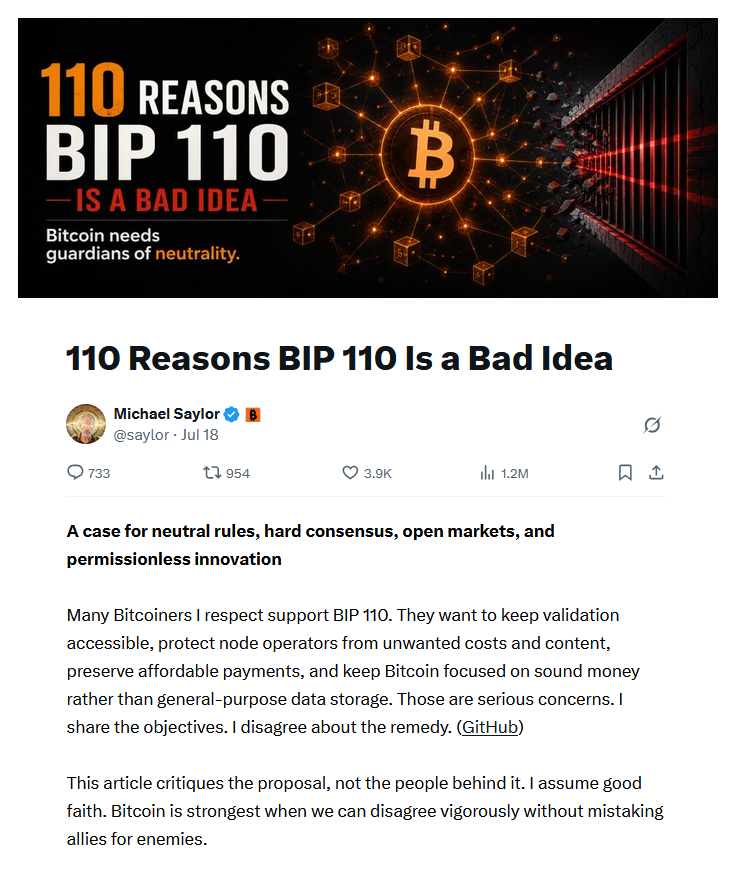
Michael Saylor and Adam Back first publicly opposed the proposal on July 11. Saylor later expanded his position in a July 18 essay titled “110 Reasons BIP-110 Is a Bad Idea,” but his intervention was part of an already active technical and governance dispute. It wasn’t its starting point.

The Bitcoin BIP-110 proposal would restrict several methods of placing large amounts of non-payment data inside transactions. Supporters argue that the limits would protect node operators and preserve block space for monetary activity. Opponents say the rules could break legitimate transaction structures and establish a precedent for judging transactions according to their purpose.

BIP-110 has not received network-wide acceptance or taken effect. Its “Complete” status means its technical specification has been finalized, not that the Bitcoin network has approved the change.

BIP-110 would impose seven temporary restrictions

Formally titled the Reduced Data Temporary Soft fork, BIP-110 would add rules that make some previously valid transactions or blocks invalid for nodes enforcing the proposal.

The proposal contains seven restrictions. They include an 83-byte limit for OP_RETURN outputs, one of several transaction fields used to attach data, as well as 256-byte caps on other data fields and tighter rules for certain Taproot scripts. Taproot is part of Bitcoin’s system for supporting more advanced transaction and contract structures.

The proposal itself acknowledges that its Taproot limits could complicate projects such as BitVM, which aims to support more complex applications using Bitcoin. Its authors also identify unusual Taproot and pre-signed transaction structures that could encounter spending problems, although they describe those cases as unlikely.

Supporters describe the targeted activity as arbitrary data storage that imposes costs on full-node operators. Every full node must download and process the blockchain. Node operators bear the verification cost, while miners receive the transaction fees.

The restrictions would apply for about one year. They would cover only UTXOs created after the activation height. A UTXO is an individual piece of bitcoin that has not yet been spent. Those confirmed before activation would remain exempt.

Dashjr and Ocean argue the restrictions are necessary

Luke Dashjr is one of the proposal’s most prominent public supporters. The Bitcoin Core developer, Ocean mining pool co-founder and technical director is credited with advising on BIP-110’s original draft.

Dashjr has presented the proposal as a defensive measure against transaction activity that he believes threatens Bitcoin’s long-term function. He has stated: “If BIP110 fails, Bitcoin fails with it.”

Ocean was the first mining pool to signal support and remains nearly the only pool doing so. Miner signalling means miners indicate support through the blocks they produce. Ocean’s position gives the proposal a named institutional advocate, although current signalling remains far below the threshold required for early lock-in.

Supporters argue that transaction fees alone do not account for every cost imposed on the network. Their case is that consensus restrictions may be justified when certain transaction structures create persistent storage and processing burdens for thousands of independent nodes.

Back and Saylor challenge purpose-based restrictions

Adam Back and Michael Saylor have emerged as the two most prominent public critics.

Back is Blockstream’s co-founder and chief executive and the inventor of Hashcash, the proof-of-work system cited directly in the Bitcoin whitepaper. He has described BIP-110 as a “literal downgrade,” arguing that it could break existing Miniscript and UTXO edge cases while creating a precedent for filtering transactions based on their perceived purpose. In practical terms, his concern is that the proposal could disrupt some advanced transaction structures that are valid under Bitcoin’s current rules.

Saylor’s July 18 essay develops a similar governance argument. He maintains that Bitcoin cannot reliably determine whether transaction data represents an image, contract, proof or future financial application. In his view, fee-paying transactions should compete for block space without consensus rules deciding whether their purpose is acceptable.

Node operators and miners can already choose which transactions they relay or include. Critics argue that converting those individual policy choices into network-wide consensus rules is a materially different step.

This is the central divide surrounding the Bitcoin BIP-110 proposal. Supporters see a temporary response to unwanted data storage. Opponents see a shift from verifying transaction validity toward regulating transaction intent.

Lopp, Todd and other critics raise broader concerns

Jameson Lopp, Casa’s chief security officer, has framed Bitcoin’s value as a “dependable anchor.” He warns that purpose-based restrictions could create a “slippery slope to centralization and control.”

Developer Peter Todd has offered a practical demonstration of another criticism: bypassability. Todd embedded the full BIP-110 text inside a transaction that complied with BIP-110’s own restrictions, illustrating that determined users may still store substantial data by restructuring how it is encoded.

Gregory Maxwell, a former Bitcoin Core developer and Blockstream co-founder, has raised technical criticisms of the proposal and has also alleged that Ocean Mining authored BIP-110. Its pseudonymous author, Dathon Ohm, denies that claim.

The August process could separate enforcing nodes

Miners began signalling support in December 2025. BIP-110 uses a 55% early lock-in threshold across a 2,016-block difficulty period. A difficulty period is a standard Bitcoin cycle covering 2,016 blocks, while early lock-in means the proposal has gained enough miner support to advance before the mandatory stage.

Signalling remained below 1% as of the weekend of July 18–19, leaving support far short of early lock-in. Miner signalling is a live figure that updates frequently and may have changed by publication.

The more contentious stage is expected around August 7, near block 961,632. Nodes running BIP-110 rules would then reject blocks that do not signal support. For that software, the specification forces lock-in by block 963,648. Activation follows near block 965,664, expected around September 1.

Those rules apply only to participating software. Nodes that do not enforce BIP-110 would continue accepting otherwise valid Bitcoin blocks. If enforcing nodes reject most blocks followed by the wider network, they could separate onto a smaller chain.

A lasting split is not certain. The outcome depends on miners, node operators, exchanges, custodians and other economically important participants. Miner signalling does not capture every form of network support.

Complete status does not represent approval

BIP editor Mark “Murch” Erhardt, who assigned BIP-110 its number, has called it “a misguided and unusually careless soft fork proposal.” He published it because it met the repository’s process criteria. But documenting a proposal and endorsing it aren’t the same thing.

BIP-110-compatible software is already available through Bitcoin Knots and several node platforms. Publishing a specification or releasing software does not equal consensus across Bitcoin.

The next meaningful evidence will come from miner signalling and adoption among exchanges, custodians and node operators. Until then, the Bitcoin BIP-110 proposal remains just that: a proposal, not an accepted upgrade for the entire network, even as its technical specification is complete and its enforcement schedule approaches.

Hidden Malware in Steam-Linked Games Led to a Federal Arrest

TL;DR

  • Federal prosecutors say malware hidden inside games listed on Steam infected about 8,000 devices, accessed around 80 crypto wallets, and stole at least $220,000.
  • Investigators say the games looked legitimate, helping the malware spread through titles promoted across major social and messaging platforms.
  • The case follows earlier public reporting on BlockBlasters and may mark the first arrest to emerge from the FBI’s broader Steam malware investigation.

Federal agents have arrested a Florida man accused of helping distribute malware through playable games linked to Steam, a popular PC game distribution platform. The alleged operation infected about 8,000 devices, accessed around 80 crypto wallets and stole at least $220,000, according to a federal complaint.

The filing states the malicious games gave the malware access to passwords, account data and crypto wallets on infected devices. Steam itself didn’t suffer any breach. 

Playable games allegedly concealed the malware

Agents arrested 21-year-old Zyaire Dontaevious Zamarion Wilkins, of North Lauderdale, Florida, on July 14. Prosecutors filed the criminal complaint in Washington state the following day. They accused Wilkins of conspiracy to obtain computer information for private financial gain.

The complaint does not name Steam directly, but refers to a popular digital distribution software company. Steam has been identified through contextual details, including the games named in the filing and the location of the case in the Western District of Washington, near Valve’s headquarters in Bellevue.

The filing says Wilkins worked with unnamed co-conspirators between approximately May 2024 and February 2026. They allegedly launched and marketed eight games containing malicious software.

How the games gained trust

The FBI’s victim-information page identifies BlockBlasters, Chemia, Dashverse/DashFPS, Lampy, Lunara, PirateFi and Tokenova. Investigators say the group promoted the games through Discord, Telegram, X and LinkedIn. 

The distribution strategy helped the malware blend in. The attackers used Steam’s reputation as a familiar place to download games, then promoted the titles on established social and messaging platforms. The installed software looked and behaved like normal games, which gave users little reason to suspect it also contained malware. 

BlockBlasters had already drawn public scrutiny before Wilkins was charged. In September 2025, independent researchers ZachXBT and vx-underground publicly linked that game to malware when a Twitch streamer raising money for cancer treatment lost roughly $32,000 during a livestream. Researchers tied that episode to more than $150,000 in estimated losses from BlockBlasters at the time.

Valve had already removed several of the flagged titles after they were identified post-launch. PirateFi was taken down in February 2025, followed by a malicious demo for Sniper: Phantom’s Resolution in March 2025, and later by Chemia and BlockBlasters in 2025. Valve has not responded to media requests for comment on that pattern, including on the Wilkins case specifically.

That exposure appears to have overlapped with the FBI Seattle field office’s public investigation into malware on Steam, announced in March 2026. This investigation also named BlockBlasters among the games under review. The July complaint appears to be the first arrest to emerge from that investigation.

The complaint alleges at least $220,000 in losses across the broader case. However, the document does not establish whether the losses reported in September 2025 are included or separate from that total.

Investigators followed the crypto spending trail

Authorities estimate that the malware reached about 8,000 devices. From those, an estimated 80 users suffered losses from their crypto wallets. Hence, not every infection led to cryptocurrency losses. 

This investigation into the malware circulating on Steam also shows how blockchain activity can connect other online activities directly to an individual. For example, agents obtained a wallet address from messages involving an alleged co-conspirator. They then traced spending from that address to Bitrefill, a service that sells gift cards for cryptocurrency.

The associated account had purchased more than 150 gift cards, including Uber Eats vouchers. Investigators then obtained account information from Uber and used it to identify a phone number and delivery address connected to Wilkins, according to the complaint.

The charges leave major questions open

The identities of the alleged co-conspirators remain undisclosed. Authorities also have not announced any recovery of the stolen cryptocurrency. The final loss could well exceed $220,000 if more victims come forward.

The FBI is now seeking information from people who downloaded the listed titles between May 2024 and January 2026. Its form asks about account compromises, missing funds, wallet addresses and transaction records. Consequently, reporting those details could help investigators identify additional victims and trace further transfers.

Visa Opens Stablecoin Platform to Selected Beta Clients

TL;DR

  • The Visa Stablecoin Platform lets selected clients test wallet, minting, transfer and redemption functions.
  • Open USD is the first supported stablecoin, but Visa does not issue the token.
  • The beta does not give Visa’s wider merchant network direct access to Open USD.

Visa has opened a new platform for selected financial institutions and fintech companies to test stablecoin operations. The service sits inside Visa’s payment infrastructure. Clients can use one environment to create wallets and manage the minting, transfer and redemption of Open USD.

The Visa Stablecoin Platform brings several previously separate technical functions together. However, it remains a limited beta, and Visa has not made the service broadly available to banks, consumers or the merchants connected to its network.

Visa packages stablecoin operations in one system

The platform, known as VSP, serves banks, fintech companies, payment providers and crypto businesses. According to Visa’s July 16 announcement, approved clients can manage stablecoins through a Visa-controlled environment. Their available functions include minting, holding, transferring and redeeming tokens.

Minting creates new stablecoin units when the required money enters the system. Burning removes units when a holder redeems them. Visa is packaging those processes with bank-account connections, wallet infrastructure and controls over who can authorize transactions.

Meanwhile, institutions can use Visa’s new Wallet-as-a-Service offering or connect wallets they already operate. The system includes audit logs, transfer allow lists and dual approvals. Under that last control, one person starts a sensitive transaction and another authorized user must approve it.

Together, these features address a practical obstacle for financial companies. A business may want to use stablecoins without building every technical and internal control itself.

Open USD is the first supported stablecoin

The Visa Stablecoin Platform begins with Open USD, or OUSD. Open Standard recently introduced the dollar-linked token with support from a group of financial, technology and crypto companies.

Visa does not issue OUSD. But, VSP connects participating institutions to the Open Standard system so they can mint, burn, manage and transfer the stablecoin.

VSP launches with support for Open USD alongside Visa’s existing support for Circle’s USDC and Paxos’ USDG through its earlier stablecoin services. Still, the company has not named which blockchain or blockchains VSP itself is using for the current tests, even though Visa’s broader stablecoin settlement infrastructure already runs on disclosed networks.

The choice also adds another competitor to the market led by Tether’s USDT and Circle’s USDC. Reportedly, Circle shares fell around 5% on July 16 as investors assessed the new competitive pressure. Only time will show whether the sentiment proves right and OUSD gains significant adoption.

The platform connects with Visa’s existing services

Visa already supports stablecoin settlement for selected partners and works with stablecoin-linked cards and blockchain-based money movement. VSP links those capabilities with the treasury and settlement systems that institutions use today.

For example, a client could link a bank account and set internal policies for stablecoin movements. It could then manage wallets and approvals through the platform. At the same time, the client could connect that activity to existing Visa services.

This approach gives institutions another way to handle money behind payment, settlement or treasury products, next to Visa’s card network. Consumers may not see the stablecoin layer at all if a bank or fintech builds it into an existing service.

Broad availability still depends on the beta

Visa’s network reaches about 15,000 financial institutions and more than 200 million merchants, according to Fortune. Should Visa decide to expand beyond the current beta, this base would be large enough that even modest adoption within VSP could translate into meaningful volume.

The company has not disclosed the names of participating institutions, transaction volumes, pricing, or a timetable for broader access. It has said, however, that beta results will determine how and where it expands the platform.

- Advertisement -

FEATURED