Home Blog Page 67

CFTC Approves First Regulated U.S. Spot Crypto Market, Reshaping Trading Structure and Resetting the Regulatory Landscape
TL;DR

  • The CFTC approved the first-ever regulated spot crypto market in the United States, enabling Bitcoin and Ethereum to trade under federal oversight without any change in existing law.
  • Bitnomial is the first exchange to launch CFTC-supervised spot trading, bringing institutional-grade custody, settlement, and market surveillance standards to the spot market.
  • The decision reshapes U.S. market structure, improves price discovery, and expands the CFTC’s practical influence over digital asset oversight as additional exchanges seek approval.

The United States has crossed a regulatory threshold years in the making. The Commodity Futures Trading Commission has approved the first-ever listed spot crypto trading on a federally supervised exchange. This decision clears the way for Bitcoin and Ethereum to trade under standards normally applied to futures markets. This marks the first time CFTC-approved spot crypto trading has entered a federal oversight regime. The decision, issued under the agency’s Acting Chairman Caroline Pham, marks a historic step forward in U.S. market structure. It establishes a regulated spot crypto market, expands institutional access, and subtly shifts the balance of crypto oversight in Washington, all without any change in U.S. law.

What Exactly Did the CFTC Approve?

The approval authorizes Bitnomial exchange to launch the first CFTC-supervised spot markets for Bitcoin and Ethereum. Rather than creating a new asset regime, the CFTC allowed the crypto exchange to list spot instruments as contracts. The listings fall under the existing framework for Designated Contract Markets. Under this structure, CFTC-approved spot crypto trading operates through listed contracts rather than informal or offshore market activity. This approach brings spot trading into the same regulatory perimeter that governs futures, which means:

  • surveillance and market-monitoring tools must already be in place,
  • clearing and custody mechanisms must meet core federal standards,
  • settlement processes require transparent risk management, and
  • reporting and compliance obligations mirror the structure applied to derivatives markets.

Crucially, the CFTC did not invoke any new statutory authority. It relied on the Commodity Exchange Act, the same legal foundation used for futures approvals, and applied it to spot contracts for the first time. The result is a market model where physical crypto settlement occurs inside a federally supervised environment rather than on offshore or lightly regulated venues.

https://twitter.com/CarolineDPham/status/1996606787089314108

Why the CFTC Could Do This Now — And Not Earlier

The biggest misconception about the approval is that the United States updated its crypto laws or resolved the longstanding SEC–CFTC jurisdiction dilemma. Neither happened. Instead, the CFTC acted because an exchange finally demonstrated that it could satisfy the 23 Core Principles required of a federally supervised trading venue.

For years, crypto exchanges lacked the custody, clearing, and compliance infrastructure necessary to qualify for listed spot markets. The CFTC could not approve what did not exist. Bitnomial became the first platform to complete the technical, legal, and operational requirements for offering physical spot settlement under federal oversight. That development created a regulatory opening the agency could act on.

The timing also reflects a shift in market expectations after several years of failures across the digital asset ecosystem. The collapse of FTX and other offshore platforms increased demand for safer market infrastructure. Against that backdrop, the CFTC moved to introduce a supervised model that enhances price discovery and restores confidence.

The decision also demonstrates regulatory continuity. Even under an Acting Chairman, the agency affirmed that it has the authority and the willingness to expand crypto oversight through established processes rather than waiting for Congress to legislate. This is how CFTC-approved spot crypto trading now, despite no legislative changes.

How This Transforms Institutional Market Structure

The launch of a federally supervised spot market represents a turning point for institutional traders. Until now, institutions could access the U.S. crypto market primarily through futures, OTC desks, or ETFs. None of those channels provided a transparent, exchange-based spot market with federal protections.

This new structure offers several advantages:

  • Orders are monitored through real-time market surveillance.
  • Custody and settlement occur within a regulated system.
  • Clearing and collateral frameworks mirror the standards used in traditional commodities.
  • Counterparty risk is reduced, encouraging broader adoption.

For funds managing compliance-sensitive mandates, this regime represents the first environment where institutional crypto trading can occur with the same oversight as other commodity markets. It also strengthens price discovery because spot markets will now operate in the same ecosystem as futures rather than being siloed offshore.

These changes may influence ETF flows as well. Analysts expect regulated spot markets to support more consistent liquidity, reduce pricing anomalies, and make benchmarks more reliable for both retail and institutional investors.

A Subtle But Significant Regulatory Power Shift

While the CFTC’s approval does not resolve the classification debate, particularly for assets other than Bitcoin and Ethereum, it does clarify part of the regulatory landscape. By enabling a supervised spot market, the CFTC has created a functioning pathway for exchanges that can meet federal obligations. As that framework expands, more of the practical oversight of crypto market structure will sit inside the CFTC’s perimeter.

This shift carries implications for the longstanding CFTC vs SEC oversight tension. The SEC continues to focus on token classification and enforcement. The CFTC is expanding supervision through market infrastructure rather than legal definitions. Exchanges, institutional traders, and policymakers will interpret this divergence as a sign that the CFTC is quietly securing influence through operational authority.

In effect, the agency has advanced regulation without redefining digital assets. It has built the architecture first and left the political debate for later. That approach gives the market clarity even as legislative gridlock persists.

What Comes Next: More Exchanges, More Assets, More Evolution

With Bitnomial as the first mover, other federally registered platforms are expected to follow. Industry observers anticipate that CME, Cboe, and Coinbase Derivatives may pursue similar approvals, which would broaden market participation and accelerate onshore liquidity migration. The U.S. regulated crypto trading landscape may soon expand beyond Bitcoin and Ethereum, though additional listings will require exchanges to prove compliance with custody and settlement standards.

The next phase of development will reveal how liquidity shifts between ETFs, futures, OTC venues, and the new spot markets. It will also test whether institutional demand increases once a safer market architecture is available.

Ultimately, the new model raises deeper questions about whether the CFTC’s approach will become a template for broader digital asset oversight. It also raises questions about how Congress will react as federal agencies continue to build structure without legislative guidance.

The approval of the first regulated U.S. spot-crypto market represents a decisive shift in American digital asset policy. It delivers a historic regulatory breakthrough, creates institution-grade trading infrastructure, and subtly rebalances authority between federal agencies, all without a single amendment to U.S. law. The arrival of CFTC-approved spot crypto trading signals a turning point in how digital assets enter federally supervised markets. As more crypto exchanges seek approval and as institutional participation increases, the United States may finally develop a cohesive market structure capable of anchoring digital asset trading inside a federally supervised framework.

Readers’ frequently asked questions

Which assets are expected to be listed first on the newly approved CFTC-regulated spot market?

The first listings are expected to be Bitcoin and Ethereum. These are the only digital assets already treated as commodities for derivatives trading, which allows them to qualify for spot listing under existing CFTC rules. Additional assets would require separate approvals and compliance demonstrations from exchanges.

Does the CFTC approval change how retail investors access crypto markets?

Not immediately. The approval creates a regulated venue for spot trading, but access still depends on whether a retail-facing platform integrates with a CFTC-registered exchange such as Bitnomial. Retail users will only experience changes once brokers or platforms begin offering regulated spot markets as part of their trading interfaces.

How can institutions participate in the new CFTC-regulated spot markets?

Institutions must onboard through a CFTC-supervised exchange or an intermediary that meets federal compliance requirements. Participation typically requires completing KYC and AML checks, meeting custody and collateral standards, and using approved clearing arrangements. Institutions cannot access the market through unregistered offshore venues if they want the protections associated with the regulated spot framework.

What Is In It For You? Action items you might want to consider

Monitor which platforms offer access to the new regulated spot markets

Bitnomial is the first exchange approved for CFTC-supervised spot crypto trading. Users and institutions should track which brokers, custodians, or trading platforms integrate this new market structure, as access will depend on which intermediaries adopt it.

Review compliance requirements before participating in regulated spot trading

Institutions must meet KYC and AML checks, custody standards, and collateral rules to participate in these markets. Traders should review onboarding requirements early, since they differ significantly from those of offshore exchanges.

Compare pricing and liquidity between regulated and unregulated markets

Once trading launches, users may observe differences in spreads, depth, and volatility between CFTC-regulated spot markets and offshore venues. Monitoring these variations can help determine when regulated markets offer better execution or reduced counterparty risk.
USPD Stablecoin Protocol Hit by $1M Exploit After Proxy Deployment Failure

Estimated reading time: 5 minutes

TL;DR

  • USPD lost around $1 million after attackers exploited a misconfigured upgradeable proxy that granted unintended access to treasury functions.
  • The team paused the protocol, secured remaining assets, and began a forensic investigation with external security partners.
  • The breach highlights recurring risks in DeFi architectures that rely on proxy-based contract upgrades and permissioning.

The USPD stablecoin hack resulted in the loss of roughly $1 million. Attackers exploited a flaw in the project’s proxy deployment architecture. The team confirmed the USPD exploit in a statement on X. They paused the protocol to prevent additional damage and launched a forensic review. Early findings suggest the vulnerability enabled unauthorized access to treasury-level permissions. The attacker drained several assets before the breach was contained.

What Happened

Reports indicate the USPD exploit stemmed from a misconfigured upgradeable proxy. The flaw allowed the attacker to gain control of critical smart contract functions. With this level of access, the malicious actor rerouted funds held by treasury contracts and moved them into external wallets. Assets involved in the $1 million stablecoin hack include USDT, USDC, WBTC, and WETH.

Suspicious activity surfaced shortly before the protocol was halted. Once the breach became clear, USPD disabled affected operations. The goal was to secure remaining reserves and stop further withdrawals. The rapid pause limited additional losses, although the full operational impact is still under review.

https://twitter.com/USPD_io/status/1996711283446464598

The Technical Root Cause

Preliminary analysis indicates a proxy deployment vulnerability in USPD’s architecture. Upgradeable proxy patterns are common in DeFi, yet they demand precise configuration. Missing or incorrect initialization steps can open unintended permission pathways. In this case, the attacker appears to have gained privileged access by exploiting the misconfigured proxy contract. That access enabled interaction with treasury mechanisms that should have remained restricted.

Researchers note that proxy-related weaknesses have contributed to several notable failures in the past. Because proxy contracts sit between user-facing logic and core functionality, even small deployment mistakes can undermine an entire protocol.

USPD’s Emergency Response

The team moved quickly to contain the incident. They froze the affected components of the protocol and secured remaining treasury balances. After confirming the breach, they notified the users. In its public statement, the team described the event as a “stablecoin protocol breach.” They also outlined ongoing cooperation with external auditors, smart-contract specialists, and on-chain investigators.

An on-chain investigation is underway. Early wallet movements have been flagged, and analysts are tracking further transfers across networks. Recovery prospects remain uncertain. The team has not provided a timeline for resuming normal operations.

Broader Implications

The incident joins a growing list of DeFi security breach cases caused by misconfigured proxy contracts. It highlights how architectural oversights can produce significant consequences, especially for stablecoin projects. These systems depend on predictable collateral management, so even small vulnerabilities can damage user trust. Smaller stablecoin projects that rely on complex upgrade paths may face heightened scrutiny after the USPD hack.

What Comes Next

USPD plans to share more information once its review concludes. For now, the protocol remains paused while the team evaluates structural fixes and long-term security measures. The USPD stablecoin hack underscores the need for rigorous audits of proxy deployments and shows how overlooked technical details can expose entire systems in fast-moving DeFi environments.

Readers’ frequently asked questions

How do proxy vulnerabilities affect stablecoin protocols from a technical perspective?

A proxy vulnerability can give unintended access to functions that sit behind an upgradeable smart-contract proxy. If these permissions are misconfigured, an attacker may interact with contract logic that was not meant to be externally accessible. This type of issue has led to more than one stablecoin protocol breach in past incidents across DeFi, according to public security reports.

What should users check when a stablecoin project reports an exploit?

Users should verify whether the project has paused operations, whether withdrawals are affected, and whether the team has shared transaction hashes linked to the incident. These steps help users determine if they are exposed to a broader DeFi security breach or if the issue is isolated to internal contracts.

How do block explorers help users understand the scale of an exploit?

Block explorers display the exact tokens and amounts transferred from a contract during an incident. By reviewing these records, users can see the value withdrawn, the destination wallets, and whether multiple assets were involved. This gives a clear and factual picture of what happened without interpreting internal project statements.

What Is In It For You? Action items you might want to consider

Review your exposure to protocols using upgradeable proxy contracts

If you interact with DeFi platforms that rely on proxy-based architectures, check whether they publish audit reports covering initialization, admin roles, and upgrade controls. This helps you understand whether similar weaknesses could affect other protocols you use.

Check whether you rely on services that integrate with USPD or its ecosystem

Some wallets, dApps, or aggregators may route transactions through affected contracts without users being aware. Verifying whether any integrated services have paused operations helps avoid failed transactions or unexpected delays.

Monitor official updates and published incident data

Usually, the protocols release exploit-related information, such as attacker addresses, paused contracts, or follow-up security measures through verified communication channels. Reviewing these updates helps you track confirmed developments instead of relying on unverified social media commentary.

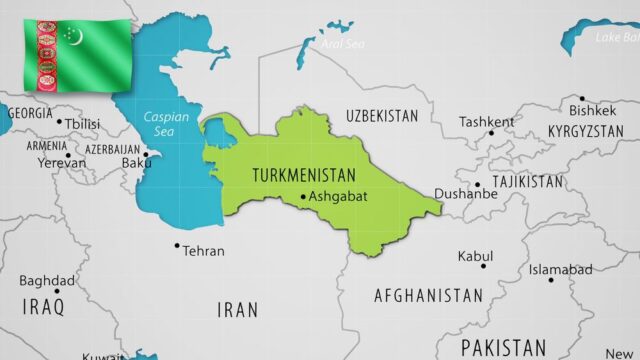
Turkmenistan Legalizes Crypto Under a New Licensing Framework Starting January 2026

Estimated reading time: 6 minutes

TL;DR

  • Turkmenistan will legalize holding, trading, and mining of digital assets starting January 1, 2026, under a new licensing framework.
  • Exchanges, custodians, and miners must register or obtain licenses from the Central Bank, while banks are explicitly barred from offering crypto services.
  • The law introduces strict advertising and branding rules and formalizes mining oversight, placing Turkmenistan within the region’s broader shift toward regulated crypto markets.

Turkmenistan has approved its first comprehensive law governing cryptocurrencies and other digital assets, establishing a licensing regime that will take effect on January 1, 2026. President Serdar Berdimuhamedov signed the legislation on November 28, 2025. With the new rules, the country moves from an unregulated environment into a supervised system that defines how digital assets may be held, mined, and traded. Turkmenistan now joins other Central Asian states that are shifting toward structured oversight of crypto activity.

What the Law Recognizes as Digital Assets

The statute introduces the term “virtual assets” and classifies them as a form of property under civil law. This designation allows individuals and companies to hold, store, transfer, and trade cryptocurrencies and other digital assets within a legal framework. The law also distinguishes between two types of tokens:

  • Backed assets, which reference fiat, commodities, or other forms of value
  • Unbacked assets, such as Bitcoin and similar cryptocurrencies

This classification sets the foundation for future technical rules that the Central Bank may introduce. However, Turkmenistan’s new crypto law does not extend digital assets to payments. Cryptocurrencies are not legal tender, and everyday consumer transactions remain outside their scope.

A Licensing System for Exchanges and Service Providers

Under the new framework, the Central Bank of Turkmenistan will oversee the licensing of crypto exchanges, custodians, and other virtual asset service providers wishing to operate in the country. The licensing regime includes requirements for:

  • customer verification and AML controls
  • custody and storage of digital assets
  • internal governance
  • reporting and record-keeping

These obligations resemble the rules used in many other jurisdictions. One clear difference, however, is the statute’s explicit ban on banks offering crypto services. Credit institutions cannot run exchanges, hold customer assets, or facilitate crypto transactions. This creates a sharper separation between banking and virtual assets than is typically seen in Europe or Asia.

The law also outlines how crypto services may be promoted. Advertising must include risk warnings and may not target minors. In addition, companies cannot use terms such as “Turkmenistan,” “Turkmen,” “state,” or “national” in branding or marketing. These restrictions are designed to prevent misleading associations with government institutions.

Mining Becomes a Regulated Industry

Turkmenistan also legalized crypto mining, although only within a structured system. Both individuals and legal entities may mine cryptocurrencies if they register their activities with state authorities. Registered miners must declare equipment, follow reporting procedures, and operate only in approved facilities. The law explicitly prohibits unregistered or hidden mining. This approach aligns Turkmenistan with regional counterparts such as Kazakhstan, where the regulation tied crypto mining oversight to energy planning and industrial policy.

By formalizing cryptocurrency mining, the law provides legal certainty for operators in Turkmenistan while giving the government a mechanism to monitor power consumption and compliance.

Part of a Regional Shift Toward Formal Crypto Regulation

Turkmenistan’s move is part of a broader trend across Central Asia. The region has moved from loosely regulated crypto activity to increasingly structured oversight. For example:

  • Uzbekistan will introduce a stablecoin payments sandbox in 2026.
  • Kazakhstan maintains a detailed licensing regime for exchanges and mining operators.
  • Kyrgyzstan has launched a state-backed stablecoin and is testing additional tokenized instruments.

Compared to its neighbors, Turkmenistan’s crypto framework is more conservative. Nevertheless, it reflects the same shift toward clear rules and supervised market activity.

Implications for Market Participants

For crypto exchanges and custodians, the new framework provides a defined path to operate legally in Turkmenistan. Licenses offer regulatory clarity, although the separation from the banking system creates a narrower operating environment.

For miners, Turkmenistan’s significant energy resources may become an advantage. At the same time, registration and reporting rules introduce administrative responsibilities that operators must meet consistently.

For individual users, crypto becomes a legally recognized asset. They will be able to hold and trade digital assets through licensed platforms, though the absence of legal-tender status means crypto remains an investment or transfer mechanism rather than a domestic payment option.

Turkmenistan’s 2026 cryptocurrency law shifts digital asset activity from a regulatory grey area into a defined legal structure. The law recognizes digital assets as property, introduces licensing obligations, and sets mining rules. Its stricter components, such as the prohibition on bank involvement and explicit advertising restrictions, distinguish it from more market-oriented frameworks. Even so, the overall direction aligns with a regional trend toward formal oversight of digital asset markets.

How quickly the sector evolves will depend on licensing implementation, infrastructure readiness, and the level of commercial interest when the framework takes effect in January 2026.

Readers’ frequently asked questions

When will individuals and companies be allowed to mine or trade crypto legally in Turkmenistan?

Crypto mining and trading become legal on January 1, 2026, when the new virtual assets law takes effect in Turkmenistan. From that date forward, individuals and companies may participate in these activities as long as they meet the licensing and registration requirements defined by the Central Bank.

Are crypto exchanges allowed to operate in Turkmenistan, and under what conditions?

Yes. Crypto exchanges may operate if they obtain a license from the Central Bank. Licensed exchanges must follow rules for customer verification, custody, governance, and reporting. Banks are not permitted to provide crypto services under the new law.

Can residents use cryptocurrencies for payments inside Turkmenistan?

No. The new law does not recognize cryptocurrencies as legal tender in Turkmenistan, and it does not authorize digital assets for domestic payments. Residents may hold, trade, and mine crypto, but everyday transactions continue to rely on the national currency.

What Is In It For You? Action items you might want to consider

Assess expansion opportunities under the new licensing framework

Exchanges and custodians should evaluate whether Turkmenistan’s upcoming licensing regime aligns with their strategic plans. The market opens on January 1, 2026, and early applicants may benefit once the Central Bank begins issuing approvals.

Review compliance requirements for mining operations

Crypto mining operators in Turkmenistan need to examine the registration, reporting, and facility-approval rules before establishing a presence. Turkmenistan’s energy profile may be attractive, but operators must comply with the formalized oversight structure.

Verify licensing when using platforms in 2026

Individual users should confirm that any exchange or service provider they choose is licensed under the new framework. Crypto becomes legally recognized property, but platforms must meet regulatory standards to operate in Turkmenistan.

Balancer DAO Approves $8 Million Payout After $128M Hack

TL;DR

  • Balancer DAO approved an $8 million reimbursement package using recovered assets and treasury funds after last month’s exploit.
  • Eligibility will be based on snapshot data taken before the attack, with automated payouts sent to active, verified addresses.
  • Distribution is expected to begin in Q4 2025 once audits and allocation contracts are finalized.

Balancer’s reimbursement plan has moved into its implementation phase after the community approved an $8 million reimbursement package for liquidity providers affected by last month’s exploit. The vote marks the first concrete round of compensation following the multi-chain attack that drained more than $120 million across several of Balancer’s vaults and forked integrations. As part of the broader reimbursement effort, the Balancer DAO aims to deliver partial relief to users while the protocol finalizes its longer-term recovery steps.

A Brief Look Back at the Exploit

The payout is rooted in the fallout of the November attack, which affected Balancer’s v2 Vaults and multiple forks. Total losses ranged from $116 million to $128 million, depending on the chain and pool tracked. Only a fraction of the stolen assets were recovered, returned, or frozen across exchanges. Those recovered tokens now form the basis of Balancer’s post-hack recovery process. The rest of the reimbursement package will come from the treasury. The community approved a supplemental allocation to cover the gaps of concentrated losses.

What Balancer’s Reimbursement Package Includes

The newly approved framework serves as the operational blueprint for compensating users. Balancer’s community has been clear that the recovery will not be full restitution. Rather, the reimbursement program will return a proportional share of recovered assets to liquidity-providers. The proposal outlines a structured recovery fund sourced from returned tokens, treasury reserves, and surplus protocol revenue. Instead of attempting to replicate complex pool states or partial LP positions, the DAO will rely on a snapshot of user balances taken shortly before the exploit.

Eligibility is determined by pool participation and verified wallet balances at the time of the attack. This structure functions as a practical payout eligibility model, allowing Balancer to offset losses without recreating each pool’s internal accounting. For many LPs, it will be the first meaningful step toward compensation after the payouts tied to the hack stalled in the immediate aftermath of the Balancer breach. Although the package accounts for only a small percentage of total losses, the plan offers clarity on how affected users will receive their share of returned funds.

How the DAO Voted

Community governance played a central role in moving the plan forward. During the DAO vote, Balancer delegates and token holders approved the reimbursement package with broad consensus. Clearly, the community is committed to stabilizing user trust. The vote also included administrative steps. It enabled the treasury to release recovered assets and authorized the use of protocol revenue. Further, it coordinated with third-party auditors to validate the reimbursement data. Governance contributors emphasized transparency and communication. They wanted to ensure users could track how the plan evolved and how the final distribution would be executed.

This governance process doubled as a stress test for Balancer’s decentralized structure. The protocol had to balance user expectations, treasury limits, and legal considerations while crafting a payout plan that could withstand scrutiny.

How the Funds Will Be Distributed

Execution will rely on a controlled treasury distribution that moves assets to a dedicated allocation contract. From there, the contract will release balances to eligible users based on snapshot data. The distribution model prioritizes stablecoins where possible, though some of the returned assets may be delivered in their native form.

The recovery fund distribution workflow includes multiple verification layers. Balancer’s core contributors have coordinated with independent auditors to review all pool data, returned tokens, and treasury allocations. A public dashboard will give LPs visibility into the dispersal process. It will display the amounts claimed, unclaimed balances, and the status of any assets still pending verification.

Community & Market Reaction

Early reaction has been cautiously positive. Many LPs expressed relief that a structured plan is moving forward, even if payouts cover only a small slice of total losses. Others noted that the recovery fund represents a meaningful attempt at user restitution in a space where many protocols historically decline compensation after exploits. Market response has been muted but stabilizing, with BAL trading within a narrow range as sentiment improves.

What Comes Next

With community approval secured, the Balancer reimbursement plan now advances to execution. Distribution is expected to begin in Q4 once audits are finalized and the allocation contract is funded. The protocol’s leadership sees this as a critical milestone in its user-compensation efforts and in rebuilding confidence after one of the year’s largest DeFi breaches.

Balancer still faces a long road toward full restoration. However, the reimbursement package marks a significant step toward honoring user losses. It also demonstrates that decentralized governance can coordinate a structured response when crises strike.

Readers’ frequently asked questions

Will users need to manually claim their reimbursement or will it be sent automatically?

Balancer plans to automate most distributions. If an eligible address still holds the same wallet, funds will be sent directly once the allocation contract is live. Only users who no longer control the original wallet, or who interacted through custodial platforms, may need to submit a manual claim later.

What happens if a liquidity provider used a DeFi aggregator like Yearn, Beefy, or Instadapp?

Aggregator users may not receive funds directly. Some platforms held LP tokens on behalf of users, so Balancer will reimburse the aggregator’s wallet. It is then up to the aggregator to pass the reimbursement to its depositors, depending on how each platform handles pooled or tokenized positions.

Will the reimbursement affect Balancer’s treasury or future development plans?

Yes. Part of the payout comes from the treasury, which reduces Balancer’s available budget for grants, liquidity incentives, and v3 development. Contributors have stated that the protocol will reevaluate spending priorities in 2026 to rebuild reserves and maintain long-term sustainability.

What Is In It For You? Action items you might want to consider

Check whether wallets used for Balancer pools are still active and accessible

If you changed wallets since the exploit or used temporary addresses, make sure you still control the original wallet. Automated distributions can only be sent to addresses that remain valid.

Contact any DeFi aggregators or vault platforms you used

If you accessed Balancer pools through platforms like Yearn, Beefy, or Instadapp, your reimbursement will go to the aggregator’s wallet. You may need to follow their internal process to receive your share.

Follow Balancer’s official governance and reimbursement updates

Monitor Balancer’s governance forum and reimbursement dashboard for inclusion lists, contract funding updates, and distribution timelines so you can confirm whether you qualify and when your payout is expected.

Upbit Hack Overshadows Naver’s Acquisition of Dunamu as ₩54B Solana Breach Halts Transfers

TL;DR

  • Upbit suffered a ₩54B ($37M) Solana hot-wallet breach, forcing an immediate halt to Solana deposits and withdrawals.
  • The incident hit hours after Naver announced its acquisition of Dunamu, overshadowing one of Korea’s biggest digital-asset deals.
  • Upbit says it will fully reimburse all user losses, while regulators intensify scrutiny amid an already tense compliance environment.

South Korea’s largest crypto exchange, Upbit, halted Solana deposits and withdrawals on Wednesday after detecting unauthorized transactions draining roughly ₩54 billion (about $37 million) from one of its operational wallets. The Upbit hack, which the exchange described as an “abnormal withdrawal activity” incident, forced the immediate freeze of Solana-network services. It also triggered a wider migration of assets into cold storage.

The breach landed at a highly sensitive moment. Just hours earlier, Naver Financial announced a stock-swap acquisition of Dunamu, Upbit’s parent company. The deal would fold South Korea’s largest crypto platform into one of the country’s most powerful tech conglomerates. Instead of dominating the news cycle, the merger was eclipsed by the exchange’s latest security failure.

A Hot-Wallet Breach Limited to Solana Assets

Upbit said the incident was contained to a single Solana hot wallet. The wallet handled daily operational flows such as customer withdrawals. The exchange confirmed that it immediately transferred all remaining Solana tokens from the wallet to cold storage after detecting the breach.

A preliminary review shows that the attackers siphoned off a wide mix of assets. These included majors like SOL and USDC, ecosystem tokens such as JUP, RAY, RENDER, ORCA and PYTH, and high-volume memecoins that trade heavily on Korean exchanges. Among them were BONK, TRUMP, MOODENG and smaller Solana-native tokens. The list aligns with on-chain tracking performed by multiple analytics firms. It also reflects user queries about which tokens were stolen in the Upbit hack.

Upbit stressed that no other networks were affected. It also said the intrusion did not compromise cold wallets, which hold the majority of customer and corporate assets.

Operational Freeze and User Assurances

Within minutes of identifying the breach, Upbit initiated a full suspension of Solana withdrawals. It also disabled deposits for all Solana-based tokens. The company moved remaining assets from its Solana hot wallet into cold storage and began working with blockchain forensics teams and Korean authorities. Investigators are now tracing the stolen funds. Early indications suggest that portions of the tokens have already been flagged or frozen on-chain.

Most critically for customers, the exchange said it will fully cover the loss using corporate reserves. Upbit emphasized that the incident will not affect user balances and also confirmed that it has reconciled all accounting for the $37M Solana breach.

This assurance is essential for South Korean users, who rely heavily on local exchanges due to the country’s closed capital system rules. Earlier exchange failures in the region, particularly during the 2022–2023 restructuring cycle, have made users wary of platform risk.

A Corporate Megadeal Collides With a Security Crisis

The most damaging aspect of the breach may not be the loss itself. Its proximity to one of the biggest corporate moves in the Korean fintech and digital-asset sector is more significant. The Naver–Dunamu merger, executed via a multibillion-dollar stock swap, aims to position Naver as a major player in blockchain infrastructure, digital identity, tokenization and AI-driven financial services.

Instead of celebrating a milestone that would make Upbit part of the Naver ecosystem, headlines quickly shifted to a security lapse at the very exchange Naver is acquiring. In a country where tech conglomerates shape national strategy, the optics were severe. Hours after one of Korea’s most influential companies announced its entry into digital assets through a high-profile merger, the centerpiece of that acquisition suffered a hot-wallet breach.

The episode complicates Naver’s narrative. The merger was designed to project institutional scale and stability. It was also intended to demonstrate readiness for regulated Web3 services. Instead, the breach revived concerns about operational vulnerabilities.

Six Years After the 2019 Upbit Hack, History Echoes

The incident also revives uncomfortable memories of the 2019 attack on Upbit. In that event, hackers stole 342,000 ETH from the exchange’s hot wallet, worth roughly ₩58 billion at the time. Korean authorities later attributed the breach to North Korea–linked groups.

There is no evidence or attribution yet for the current attack. Even so, the recurrence, ie, similar month, similar wallet tier, similar operational vectors, adds symbolic weight. Korean media quickly noted the six-year parallel. They also pointed out that the new breach arrives just as Upbit is being absorbed into a larger corporate structure.

Regulators Were Already Watching Closely

The timing intersects with an already tense regulatory environment. Upbit recently received a fine from Korea’s FIU and a temporary three-month ban on onboarding new users. The enforcement campaign aims to tighten domestic compliance frameworks. Regulators have also been vocal about hot-wallet risk, exchange liquidity transparency and the need for real-time monitoring tools.

The new incident will likely accelerate discussions over how Korea will regulate exchanges after the Upbit hack. Lawmakers could consider stricter caps on hot-wallet balances and mandatory cyber-insurance requirements. They may also push for expanded oversight of operational security practices. With the incoming Naver–Dunamu consolidation, regulators are likely to ask how the merged entity plans to enforce safety across a larger financial ecosystem.

Market Reaction: Contained and Exchange-Specific

Despite the size of the loss, market reaction across the Solana ecosystem remained contained. SOL traded within a narrow band following the news. The SOL price reaction was muted for an event involving a top Asian exchange.

Memecoins such as BONK, TRUMP and MOODENG saw brief intraday swings. They avoided the kind of cascading sell-offs associated with protocol-level failures. Analysts noted that the impact of Upbit hack on the Solana ecosystem was minimal because the event was clearly exchange-specific. It did not indicate an issue with Solana’s consensus or security model.

This decoupling reflects a growing maturity in crypto markets. Investors increasingly distinguish between operational risks at centralized exchanges and vulnerabilities within blockchain networks.

What Comes Next

Upbit says it will restore Solana transactions once security reviews are complete. It has not provided a specific timeline. Investigators are tracing the stolen funds across multiple addresses. Korean authorities are conducting a formal review of Upbit’s systems and incident response procedures.

Naver now faces an early stress test of an acquisition meant to expand its presence in digital finance and Web3 infrastructure. Regulators, meanwhile, are likely to treat the incident as a catalyst for tighter oversight. And users will ultimately judge Upbit on one metric only: whether the exchange fully compensates every loss.

The merger may reshape Korea’s digital-asset landscape. Even so, the timing of this breach ensures that the road to integration begins under scrutiny rather than celebration.

Readers’ frequently asked questions

When will Upbit lift the Solana withdrawal suspension, and how will users know the service has resumed?

Upbit has not provided a specific timeline for restoring Solana deposits and withdrawals. The exchange will resume services only after completing internal security checks, wallet infrastructure reviews, and coordination with blockchain forensics teams. Users will receive updates through Upbit’s official notice board, mobile app notifications, and the Solana deposit/withdrawal status page inside the exchange.

Did the hack affect specific Solana tokens, and where can users check which assets were stolen?

Yes. The breach involved a range of Solana-based assets including SOL, USDC, JUP, RAY, RENDER, ORCA, PYTH, and several Solana memecoins. Users can verify the affected tokens by checking Upbit’s official security incident notice or by reviewing on-chain tracking reports published by blockchain analytics firms after the breach.

Did the breach have any impact on Solana’s network or ecosystem, and should holders expect disruptions?

No. The hack was limited to an Upbit operational wallet and did not affect Solana’s network, validators, or protocol security. Holders should not expect disruptions to SOL trading, transfers, or ecosystem activity. Market reaction has been minimal. It seems that the public perceives the event as an exchange-specific incident rather than an issue within the Solana ecosystem.

What Is In It For You? Action items you might want to consider

Monitor Upbit’s Solana service status

Keep an eye on Upbit’s official notices to see when Solana deposits and withdrawals reopen and whether any additional verification steps are required after the security review.

Review your recent Solana transactions

Check your recent deposit and withdrawal history for Solana-based assets on Upbit. Even though user funds are protected, confirming that your recent activity appears accurate can help surface any irregularities.

Strengthen your Upbit account security

Enable features such as withdrawal whitelists, two-factor authentication, and device verification. These settings reduce the risk of unauthorized activity while Upbit completes its internal security upgrades.

- Advertisement -

FEATURED